WordPress Form Honeypot: Stop Spam Bots Without a Captcha
How the ReportedIP Hive form honeypot and execution proof stop spam bots on comments, sign-ups and form plugins, what a refused visitor sees and what each plan covers.
Read moreRelease announcements, threat intelligence updates, and security news from the ReportedIP team.
How the ReportedIP Hive form honeypot and execution proof stop spam bots on comments, sign-ups and form plugins, what a refused visitor sees and what each plan covers.
Read moreHive 2.1.53 added a form execution proof against scripted comment, sign-up and password-reset spam, and 2.1.54 replaced the ten-step setup wizard with a one-page quickstart. With notes on what has changed up to 2.1.67.
Read moreHive 2.1.51 brought registration rules, access lockdown switches, a readiness register, adaptive two-factor triggers and account blocking with a session manager. Three of the five are free on every plan. With notes on what has changed up to 2.1.67.
Read more21 new WordPress honeypots nobody knew about took 356 attacks from 84 IPs in seven hours on 6 September 2026. The first attack came 15 minutes after go-live.
Read moreCVE-2026-19949 lets attackers plant SQL in trackbacks that fires when a backup is restored in All-in-One WP Migration up to 7.109. Affected versions, the fix in 7.110, how to spot an attack and what the Hive firewall covers.
Read moreNine security findings closed, plugin updates restored for remote dashboards, one settings registry and signed fleet management for every site you run. What Hive 2.1.42 to 2.1.49 shipped, with notes on what has changed up to 2.1.67.
Read moreFour months after its first release, 88 WordPress sites had connected ReportedIP Hive to the community network by August 20, 2026. The HIVE50 coupon takes 50% off the first year of Hive PRO until November 20, 2026.
Read moreWhen blocking Tor exit nodes in WordPress makes sense, how ReportedIP Hive does it, where the limits are and how to set up the real client IP behind Cloudflare.
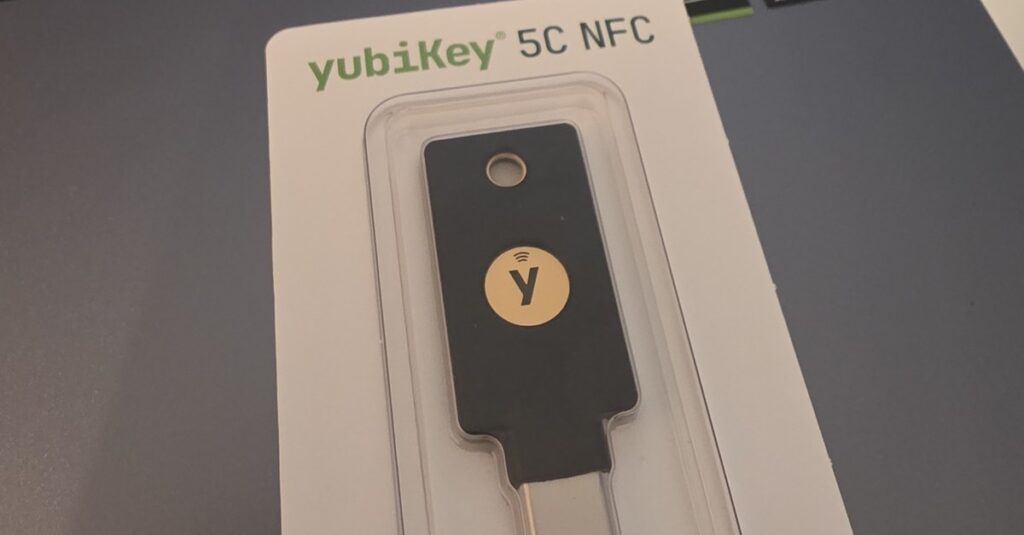
Read moreHow to use the YubiKey 5C NFC as a second factor in WordPress with ReportedIP Hive: setup, USB-C and NFC login, lost keys and the error messages you will meet.
Read moreFrom May 1 to July 21, 2026, the ReportedIP network recorded 1,692,650 attacks from 206,388 unique IPs. Login brute force led the WordPress categories, and wp2shell showed up in the data.
Read moreSync the ReportedIP blacklist into ipset or nftables yourself: five port-scoped lists, hourly ETag polling that costs no quota, fail2ban reports back, and when the Linux Agent is the better route.
Read morewp2shell chains two WordPress core CVEs into unauthenticated code execution. Affected and fixed versions, 601 attack reports from our honeypots and how Hive blocks it on every plan.
Read more