Setting Up WordPress Security in Minutes: The ReportedIP Hive Quickstart
A one-page quickstart with privacy-first defaults configures sensors, 2FA, retention and a real-time dashboard, your site is protected before the coffee is cold.
Real-time IP reputation from a community threat network, eighteen attack sensors incl. a Web Application Firewall and four-method two-factor authentication. Open-source core, EU-hosted relay, GDPR-ready DPA, built and operated in Germany.
The plugin itself is free: full local protection, no signup, no account. Paid plans add the managed relay. Compare plans
Every attack vector that hits a WordPress site has a dedicated sensor with tunable thresholds. None of them require the community network, they all work in Local Shield mode. The table shows the most common ones; the complete list of all 18 sensors, including the Web Application Firewall, is in the plugin documentation.
| Sensor | Default threshold | What it catches |
|---|---|---|
| Failed Logins | 5 / 15 min | Brute-force protection on wp-login, REST, and XML-RPC. |
| Password Spray | 5 distinct usernames / 10 min | Hash-based detection of attackers cycling usernames. |
| Comment Spam | 5 / 60 min | Automated comment-form spam detection. |
| XML-RPC Abuse | 10 / 60 min | system.multicall amplification + repeated wp.getUsers tracked separately. |
| App-Password Abuse | 5 / 15 min | REST/XML-RPC bypass attempts against application passwords. |
| REST API Rate-Limit | 240 global / 20 sensitive / 5 min | Public REST flood with auth-user bypass. |
| User Enumeration | First probe blocks | ?author=, /wp-json/wp/v2/users, oEmbed disclosure. |
| Scanner / 404 | 12 / 2 min + instant on known-bad | .env, wp-config.bak, /.git/, plugin paths. |
| Geographic Anomaly | First occurrence | New country / continent triggers fresh 2FA challenge. |
| Password Policy | Configurable | Length, char classes, optional HIBP k-anonymity check. |
| WooCommerce Login | 5 / 15 min (separate) | my-account & checkout pages tracked independently. |
| Consent Endpoints | Always bypassed | Real Cookie Banner, Complianz, Borlabs, CookieYes, baked-in. |
Released 10 to 13 September 2026 across two versions: a spam-defence layer and a rebuilt first day. All five changes are free on every plan.
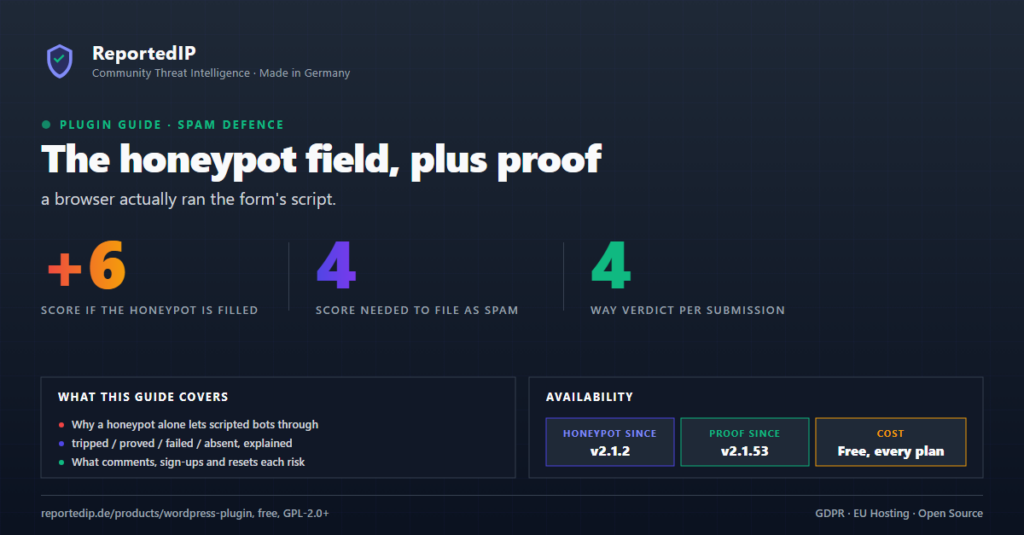
A hidden anchor field plus a script-added twin, named differently per install, sort every comment, sign-up and password-reset submission into one of four verdicts. A submission that never ran the page’s script scores against the spam threshold instead of an outright block.
The reputation check that has run on the login page since the first release now covers comments, sign-ups and password resets too, at the same floor and hardening clamp, and fails open on a quota or timeout exactly like the login page always did.
One quickstart page asks for the mode and a Community Access Key, reads the plan from the key check, and applies a plan-aware recommendation through the settings registry. Three switches stay visible; everything else is preconfigured.
Tor blocking, the HSTS header and 90 days of logs on Professional, a one-year audit trail on Business, applied automatically to every setting the admin has not changed by hand, with a banner listing what changed.
Eight options that used to live outside the settings registry, upgrade hints, quota and plan-change mails, the 2FA reminder settings among them, now export, import and sync through MainWP and the cloud fleet like every other setting.
All four methods live in the core. TOTP, Email and WebAuthn work on every plan including Free; SMS delivery runs over our managed EU relay (Professional and up, no Twilio or third-party account needed). Plus 10 single-use recovery codes, trusted-device support (auto-revoked on geo anomaly), and a password-reset gate that requires non-email 2FA before a new password is accepted.
Authenticator App
Time-based codes that work offline. Compatible with Google Authenticator, Authy, 1Password, Microsoft Authenticator. Secrets encrypted at rest. RFC 6238.
6-digit Code
Falls back to local wp_mail() in Local Shield, switches to managed relay on Pro+ for guaranteed delivery. Rate-limited, hashed storage.
Managed EU Relay
Delivered over the managed reportedIP relay (Professional and up): EU-only sub-processor, signed DPA, no Twilio account. Rate-limited, phone numbers encrypted at rest.
Passkey / Hardware Key
Phishing-resistant. Official YubiKey support (USB-C / NFC), Face ID, Touch ID, Windows Hello. ES256, RS256 and Ed25519, cloned-key detection, multi-key manager. No external dependencies.
A stolen mailbox should not be a master key to your WordPress site. Hive wraps the lost-password flow with the same 2FA gate as the login, and the recovery channel (email) is excluded from the eligible methods, because the reset link itself arrives by email.
Email excluded from reset 2FA
A compromised mailbox cannot double as the second factor. The reset link and the 2FA confirmation must arrive on different channels: TOTP, Passkey, SMS or a single-use recovery code.
Two-stage WordPress hook
Gated twice, once when the reset form loads, once at password_reset. A direct POST against the reset form without a verified token returns WP_Error immediately.
Bound to user + key + IP
The verified-reset transient is scoped to user ID, the hashed reset key and the hashed client IP. Consumed on first use, expires after 10 minutes.
No separate brute-force surface
Failed reset-challenge attempts feed the same IP throttle that already shields wp-login.php. Optional hard-block for accounts that only have email-2FA, admin notification included.
Default is fully offline. The community network is opt-in and never mandatory.
All 18 sensors and the full 2FA suite run locally on your own server. No external calls, no telemetry, no API key.
Default after install. Switch any time.
Pre-auth IP reputation lookups against the public database. Coordinated-attack detection across thousands of sites. Anonymised reports flow back so every attack makes the network smarter.
Free account at reportedip.com required. Free forever.
We sweat the small stuff so you don’t have to defend the choice in front of a DPO.
Just the attacker’s IP, a threat-category tag (failed_login, comment_spam, etc.), and a timestamp. No usernames, no comment bodies, no request payloads, no user-agents. The network needs to know that an IP attacked, not how or who. Mail and SMS relay run on EU-only sub-processors under signed DPA. Every request also identifies the installation itself, the site address and the plugin/WordPress version, wp.org-style, so domains can be counted against your plan. Visitor-related data stays limited to the IP address and event type of a detected threat.
Three protection layers, each on the right tier, failure tracking on Free, themed Frontend 2FA from Professional, full white-label integration on Business.
Failed customer logins on /my-account/ and checkout-form abuse feed the same brute-force counter as wp-login attempts, on every plan, including Free. Hooks: woocommerce_login_failed and woocommerce_checkout_login_form_failed_login.
The second factor renders inside your active theme. No wp-login bouncer, no “log in to wp-admin to verify” detour. Customer self-service on a configurable setup slug (default reportedip-hive-2fa-setup), never inside /wp-admin/. Cart and checkout state survive the redirect roundtrip; the trusted-device cookie is shared with the wp-login flow.
White-label quickstart, themed mail templates, and Subscriptions / Memberships audit. Agencies ship Hive under their own brand, customers never see “ReportedIP” until the support escalation page.
Run more than one WordPress site? Steer Hive across your whole fleet from a single dashboard, define one security policy, override single fields per site, push it with one click, and see instantly when a site drifts from the policy.
Hive carries its own MainWP child bridge. Connect a site to your MainWP dashboard as usual and manage its security settings centrally, fleet-wide status at a glance, one-click access-key provisioning, and centrally managed policies. Data-minimised: the sync returns counts only, never IP addresses, usernames or secrets.
On the Business plan, manage the same settings straight from your reportedip.com account under Domains, no MainWP required. Strictly opt-in per site (a toggle on the General settings tab, off by default). Every push is cryptographically signed, bound to your site and account, replay-protected, and refused unless it verifies.
Both dashboards manage the same 169 settings across every group, detection, blocking, WAF, hide-login, account security, privacy and notifications, through the same validation pipeline, so a policy behaves identically wherever it is applied. Each site reports a settings fingerprint, so a change made directly on a site shows up as drift until you push again. “Push drifted only” heals exactly the sites that need it.
Most security plugins are licensed per single site. Hive is licensed per plan, so the more sites you run, the less each one costs. Every price includes 19 % VAT; Enterprise is quoted net (B2B).
| Plan | Price | Sites | € / domain | Highlights |
|---|---|---|---|---|
| Free | 0 € | 1 | 0 € | All 18 sensors incl. WAF + 2FA, Local Shield |
| Professional | 14.90 €/mo | 3 | 4.97 € | Managed mail/SMS relay, Hardening Mode |
| Business | 39 €/mo | 15 | 2.60 € | White-label, full WP-CLI, GDPR export |
| Enterprise | from 663 €/mo (net) | unlimited | – | Custom AVV, dedicated onboarding |
Every sensor and every 2FA method lives in the open-source core and stays free. Paid plans add managed mail/SMS delivery, multi-site licensing and higher API quotas, never the security itself. The relay runs on EU-only sub-processors under signed DPA. Annual billing saves 17 % (149 €/yr Professional, 389 €/yr Business).
Competitors license per single site, so their price per domain never drops. List prices as of April 2026, USD converted to euro, gross where a vendor sells to consumers.
| Plugin | € / domain / month | 2FA mail relay | SMS 2FA | Rules held back on the free tier |
|---|---|---|---|---|
| ReportedIP Hive Professional | 4.97 € | Included, 500/month | Included, 25/month | Nothing held back |
| ReportedIP Hive Business | 2.60 € | Included, 2,500/month | Included, 75/month | Nothing held back |
| Wordfence Premium | 8.30 € | No | No | Firewall rules and malware signatures 30 days late |
| Solid Security Pro | 8.30 € | No | No | Yes |
| WP 2FA Premium | 8.30 € | No | Only with your own Twilio account | Yes |
| MalCare Pro | 11.75 € | No | No | Yes |
| Patchstack Plus | 17.00 € | No | No | Yes |
Every vendor named here runs on US infrastructure. Hive stores and processes in the EU under a signed DPA. Read the full Hive and Wordfence comparison.
The core protection is identical on every tier. Paid plans add managed mail/SMS relay, multi-site licensing and higher API quotas, never the security itself. All prices incl. 19 % VAT.
The Hive plugin is free and open source forever, and the free tier already includes the public API with 1,000 checks a day. Paid plans add managed 2FA mail and SMS relay, multi-site management, and higher API quotas.
Local protection, free forever
Solo developers and small sites
14-day money-back guarantee. Cancel anytime.
Agencies, WooCommerce, white-label
14-day money-back guarantee. Cancel anytime.
Includes Contributor and Enterprise tiers plus the full feature comparison table.
Built for freelancers and agencies who secure more than one WordPress site.
No Composer, no build step, no external dependencies. The quickstart takes care of the rest.
In WP Admin: Plugins → Add New → Upload Plugin. Pick the ZIP, activate. The quickstart opens automatically.
Pick Local Shield or Community Network. Enable 2FA roles. Done. Auto-updates via the GitHub Plugin Update Checker (PUC v5.6+).
Specific to the WordPress plugin. For platform-wide questions see the general FAQ.
Yes. Hive activates network-wide and tracks attacks per-site, with optional global blocklist sharing across the network. Multi-site licence (Hive Pro = 3 sites, Business = 15 sites) controls how many independent sites can use the managed mail/SMS relay.
Hive looks for a new version every 12 hours and offers it in your WordPress dashboard, exactly like any other plugin. One click and you are up to date. After the first install you never download a file again.
No. Sensor counters use object cache (Redis when available) with millisecond lookups. Reputation API responses are cached locally with ETag support to save credits. The admin dashboard loads on demand, never on the front-end.
Yes. All plugin admin and login pages are excluded from page cache automatically. Reputation lookups happen server-side before WordPress renders, so cached pages are served untouched. We test against WP Rocket every release.
Yes. Every list table (Blocked IPs, Whitelist, Logs, API Queue, 2FA Grid) supports CSV and JSON export from the admin UI. WP-CLI commands cover the same operations for automation (full WP-CLI on Business+).
The protection is never paywalled: all eighteen sensors are in the open-source core and free forever, on every plan, along with TOTP, email and WebAuthn 2FA; SMS 2FA is delivered over the managed relay on Professional and up. Paid plans (Professional 14.90 €/mo, Business 39 €/mo) add the convenience layer, managed 2FA mail and SMS delivery, multi-site licensing (3 or 15 domains on one licence), higher API quotas, Hardening Mode, white-label and full WP-CLI. All prices incl. 19 % VAT.
You can run the free edition indefinitely. Paid plans come with a voluntary 14-day money-back guarantee (under § 12 of our Terms, excluding already-consumed SMS or mail bundle credits) and you can cancel any time from the dashboard.
Three sites for 14.90 €/mo, managed 2FA delivery, multi-site licensing and Hardening Mode. 14-day money-back, cancel any time.